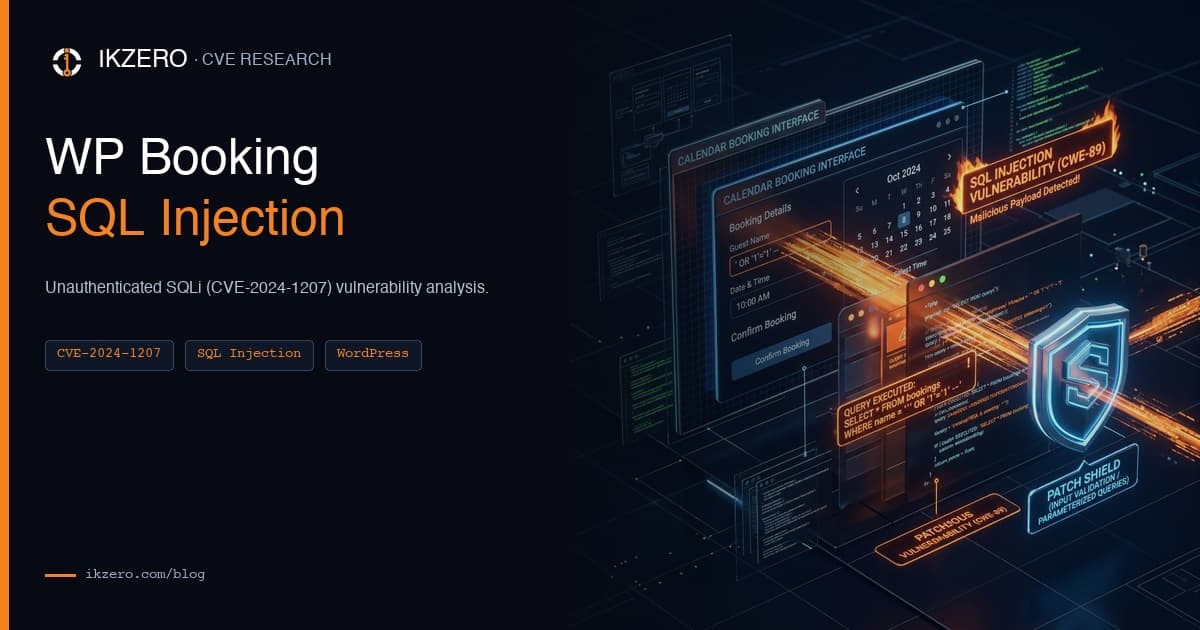
As part of our ongoing commitment to making the internet safer, Ikzero actively participates in responsible vulnerability disclosure programs. In early 2024, our Principal Consultant, Muhammad Hassham Nagori, discovered CVE-2024-1207, a critical, unauthenticated SQL injection (CVSS 9.8) in the widely used WP Booking Calendar WordPress plugin, installed on over 60,000 websites.
Because the flaw required no authentication whatsoever, any anonymous visitor could exploit it, making it far more dangerous than a typical authenticated bug. It was responsibly disclosed through the Wordfence Bug Bounty Program and assigned CVE-2024-1207.
Vulnerability Summary
Plugin WP Booking Calendar by wpdevelop
Vulnerability Unauthenticated SQL Injection
CVE CVE-2024-1207
Affected Versions Up to and including 9.9
Patched Version Fixed by the vendor in the release following disclosure
Severity Critical (CVSS 9.8)
Reported Via Wordfence Bug Bounty Program
Discovered By Muhammad Hassham Nagori (Principal Consultant, Ikzero)
Technical Analysis
During independent security research, our Principal Consultant identified that the calendar_request_params[dates_ddmmyy_csv] parameter was insufficiently escaped and passed into a SQL query without adequate preparation. Because this code path was reachable without any login, an unauthenticated attacker could inject arbitrary SQL directly into the plugin's database queries.
This is the most severe class of web vulnerability: no credentials, no user interaction, and a direct line to the database.
Impact Assessment
-
Anonymous and mass-exploitable: No account needed; every affected site was reachable by anyone on the internet
-
Full database extraction: Administrator credentials, customer booking details, emails, and personal data at risk
-
Credential theft: Admin password hashes could be dumped and cracked offline
-
Full site takeover: Extracted admin access leads to complete WordPress compromise
-
Regulatory exposure: GDPR and PDPL implications for any business handling customer data
Responsible Disclosure Timeline
-
Discovery: Vulnerability identified by our Principal Consultant during independent research
-
Disclosure: Responsibly reported through the Wordfence Bug Bounty Program
-
Vendor Response: The plugin author acknowledged the report and developed a fix
-
Patch Released: A hardened version was published to close the injection
-
Firewall Protection: Wordfence deployed WAF rules to protect users ahead of patch adoption
Lessons for Website Owners
-
Unauthenticated bugs are urgent: When no login is required, patch windows matter in hours, not weeks
-
Update plugins immediately: Published CVEs are actively scanned for by attackers
-
Deploy a Web Application Firewall: Virtual patching buys you time while you update
-
Audit your plugin stack: Booking, form, and calendar plugins handle untrusted input and are common targets
-
Invest in manual security testing: Parameter-level injection like this is routinely missed by automated scanners
Why This Matters for Your Business
When you work with Ikzero, you are working with a team that actively discovers zero-day vulnerabilities in production software used by tens of thousands of businesses. Our Principal Consultant applies the same deep, manual analysis to every penetration test and secure build we deliver.
Is Your Web Application Secure?
Vulnerabilities like this could be lurking in your stack right now. Schedule a free security consultation with our team today, or explore our penetration testing services.
Reference: Wordfence Intelligence: Booking Calendar ≤ 9.9 Unauthenticated SQL Injection (CVE-2024-1207)